CVE vulnerabilities
Published CVE that target the versions you run, ranked by exposure.
At a glance
- WhereSecurity, then CVE Vulnerabilities.
- AccessCompliance module and audit permission.
- DataThe collected versions, and an HTTPS path out to our service for the catalogue.
What the screen shows
What you can do
- 1
Update the catalogue
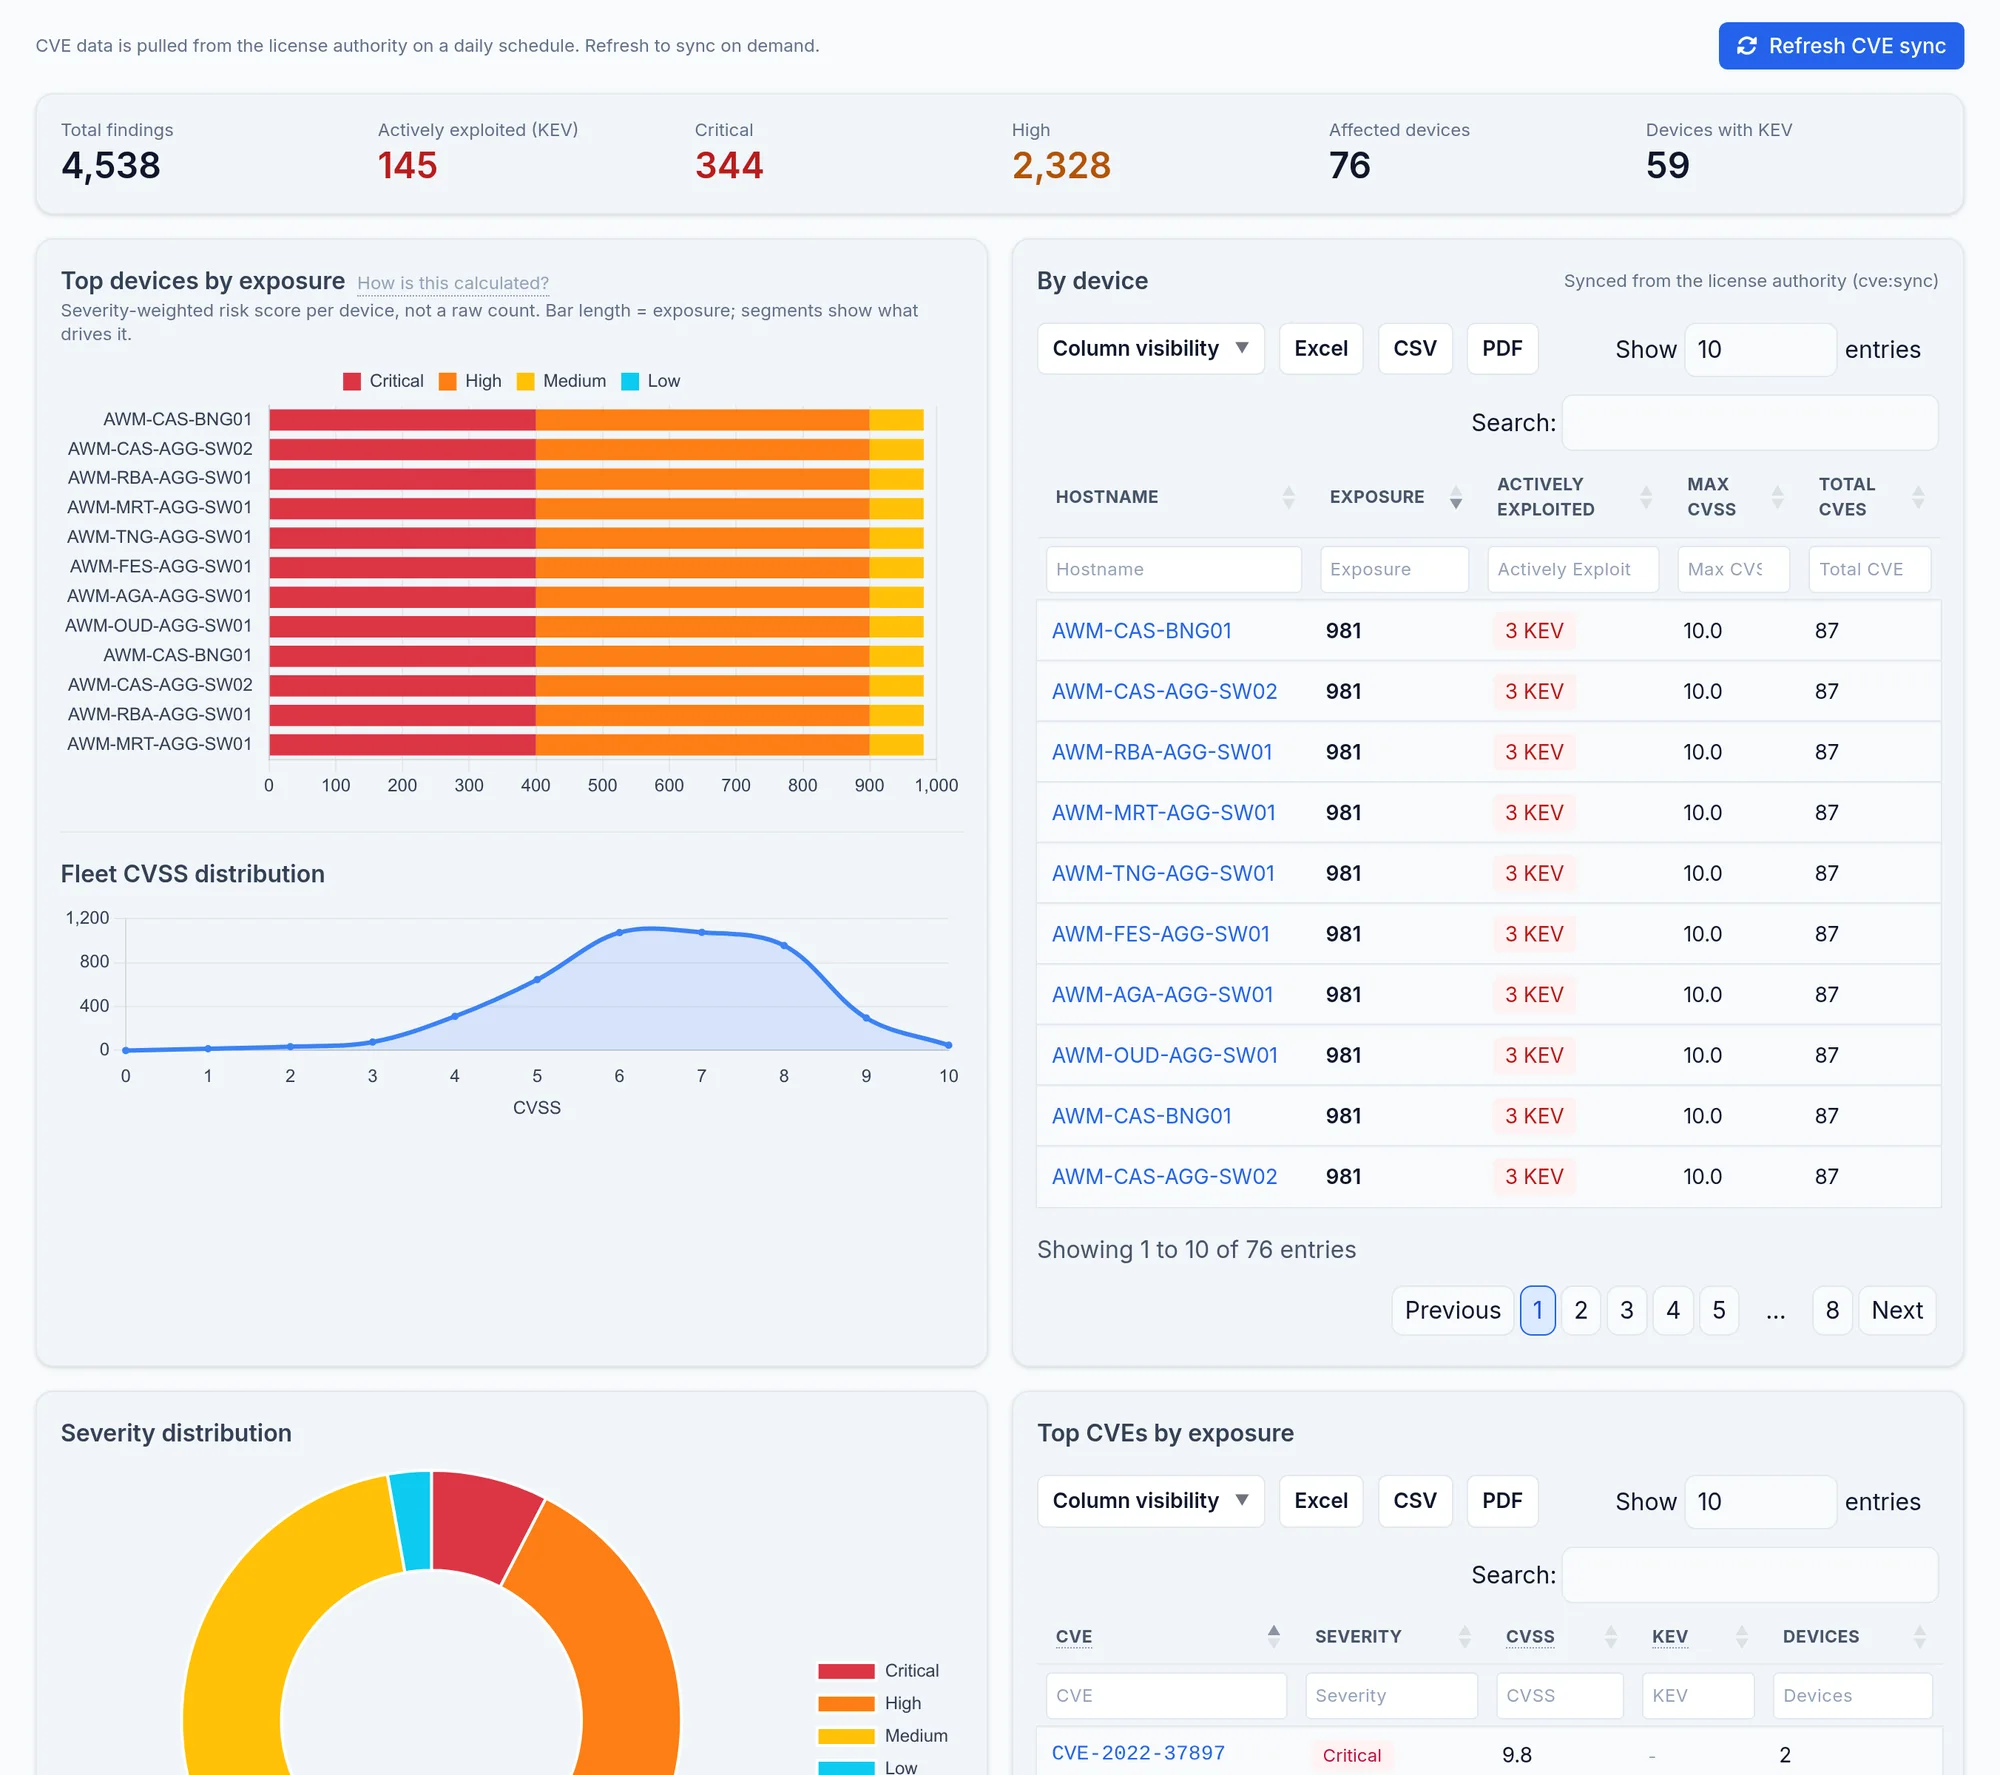
Refresh CVE sync starts synchronisation in the background; it also runs every night. The page shows the last attempt's result.
Limits and things to know
What leaves the appliance?
For each vendor, system and version combination, the device count. No device name, address or identifier.
A CVE is not a proven flaw
Matching is by version: the device is potentially affected, the configuration may not use the vulnerable feature.
Read next
How to tell whether a Cisco IOS XE version is affected by a CVE
Match a Cisco IOS XE release against Cisco advisories for every device at once, then check the configuration conditions the match cannot see.
ManualEOL lifecycle
The end of sale and end of support dates of your models, the devices at risk within 180 days, and how the lifecycle catalogue updates.
ManualCompliance
How to run rule evaluation, read the estate and per device scores, set a waiver on a check, and export the findings as PDF, XLSX or CSV.