Put the whole estate through named rules
Every configuration is scored against named rules. Each gap comes back with the rule that caught it, the device it sits on and the date it was seen.
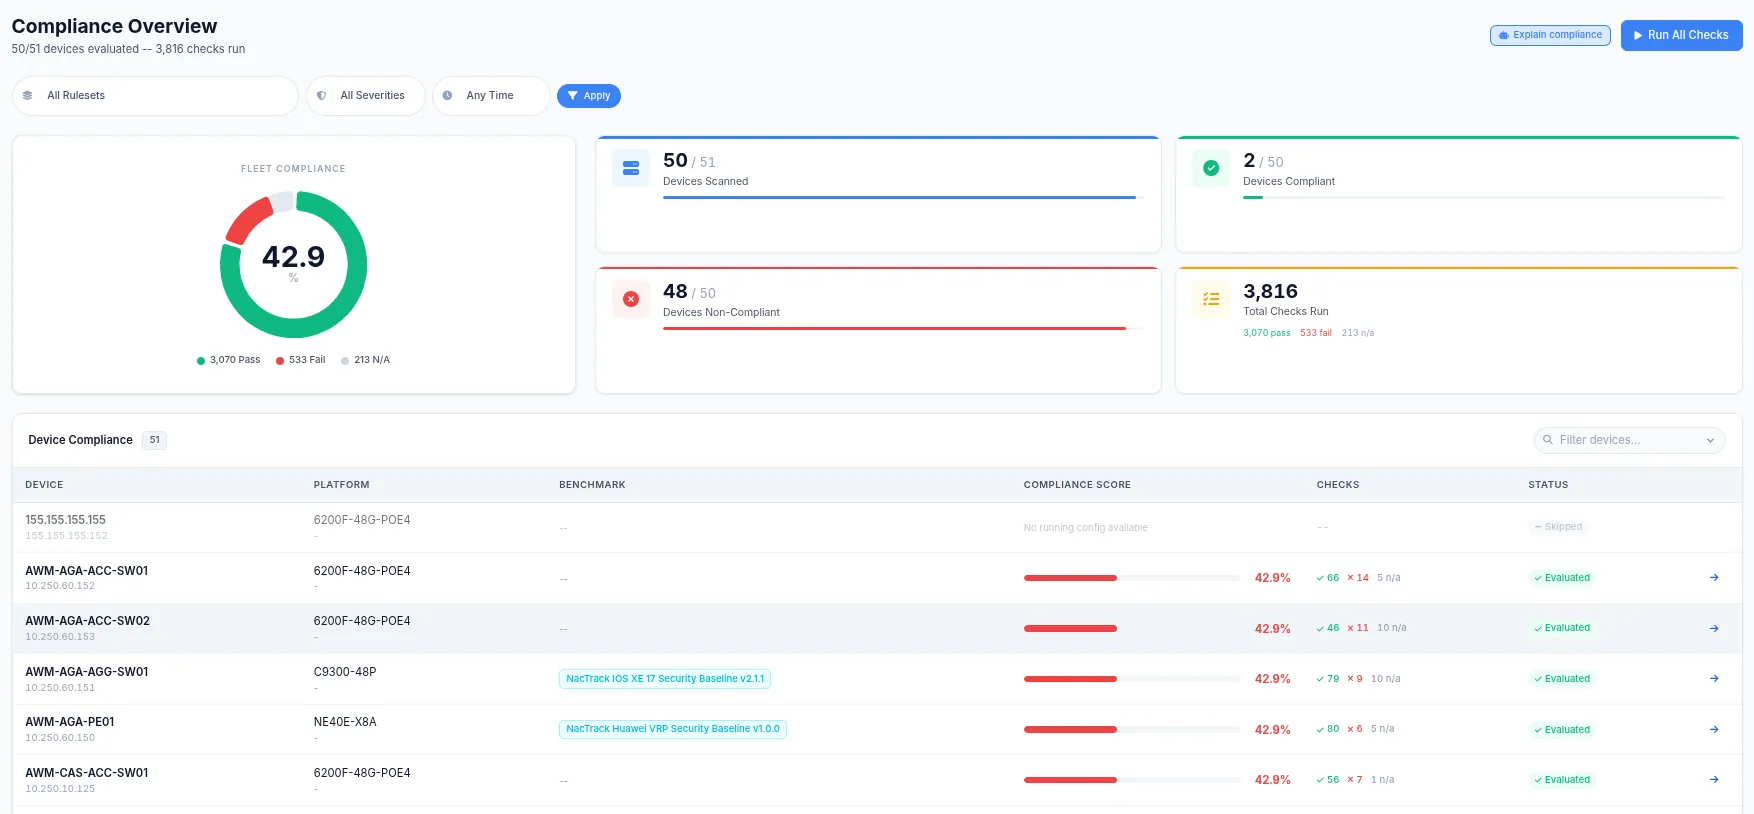
A named rule, not an impression
The word weak cannot be measured. An explicit rule can.
- Default SNMP community present. Version 2c allowed. Write community.
- VTY line accepting Telnet. No ACL on administrative access.
- No session timeout set. Password stored in clear in the configuration.
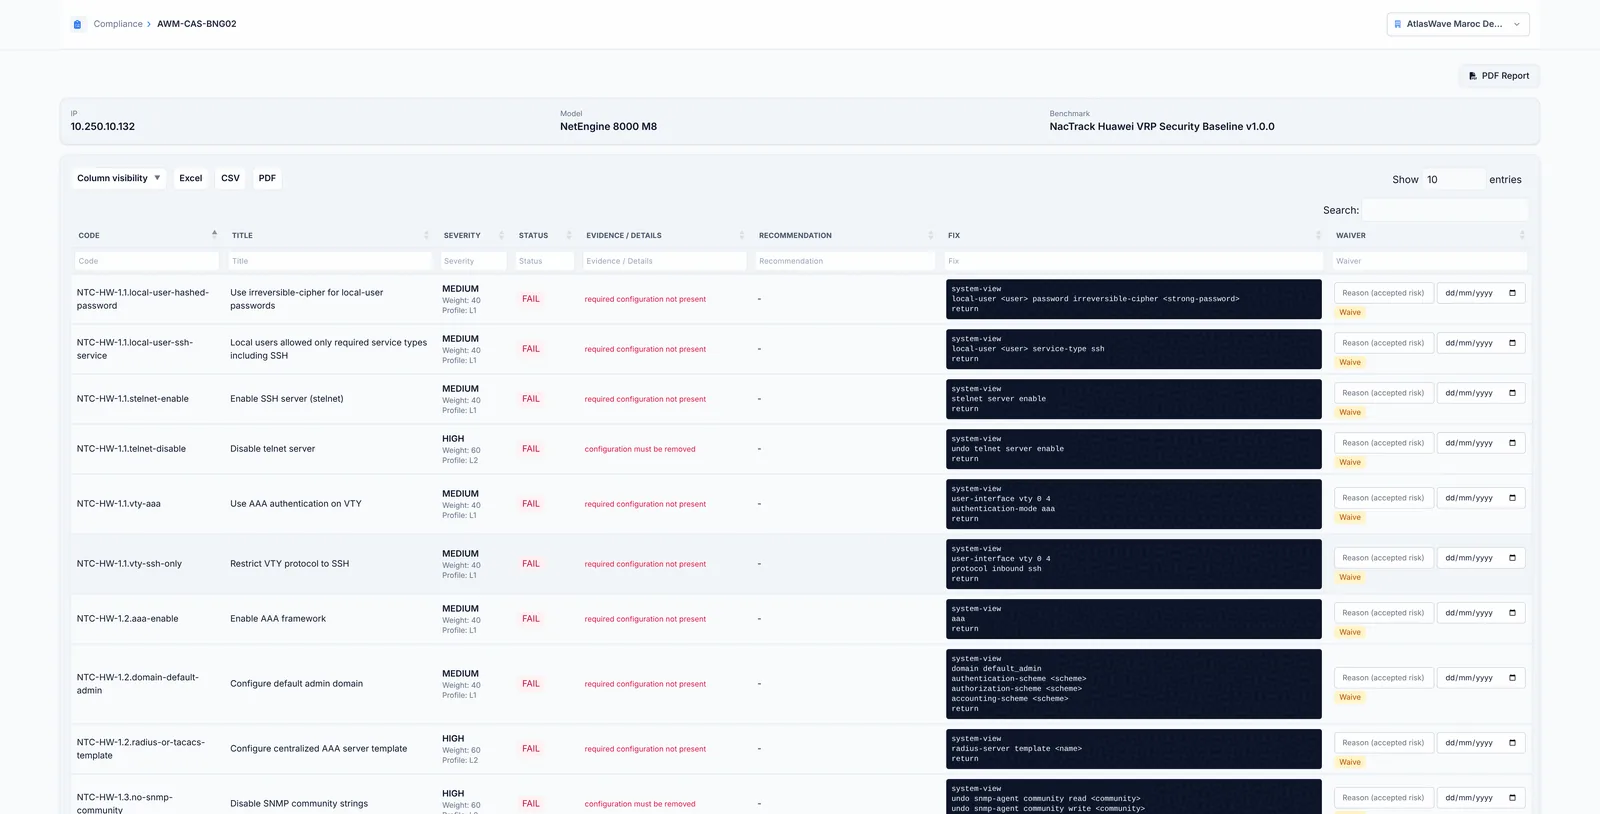
- Every finding carries the rule code, its severity, the exact configuration extract that triggers it and the recommended fix.
- The rule sets that ship derive from public hardening baselines and are adapted per platform: a rule written for Cisco and applied as is to VRP measures nothing.
- The rule sets evaluate configuration text: they describe what the configuration allows, never what a running session is actually doing.
What the evaluation covers
Management plane
Administrative protocols allowed, separation into a dedicated VRF, ACL applied, banner, session timeout.
Authentication
AAA, TACACS or RADIUS servers, local accounts, password policy, SSH retry limits.
Logging and time
Logging servers, timestamps, NTP, without which no later investigation is possible.
SNMP
Default communities, allowed versions, write access, ACL restriction.
Remote access
Telnet, plain HTTP, SSH versions, what remains open on management interfaces.
What the finding carries
A dated report, per device and per rule, exportable for a committee or a regulator.
Have your estate evaluated
One day, read only, and a report that belongs to you.