One day, your estate, one report
Once read access is open, we collect your own network in a day, on your own infrastructure, and hand you the report. No commitment, no purchase order.
How it runs
- 1
You give us read access
A read only account on the devices, from your management network. No write access is requested, and no configuration is changed.
- 2
We collect
Collection completes within the day on an estate of usual size. Nothing is installed on the devices and the data plane is untouched.
- 3
You receive the report
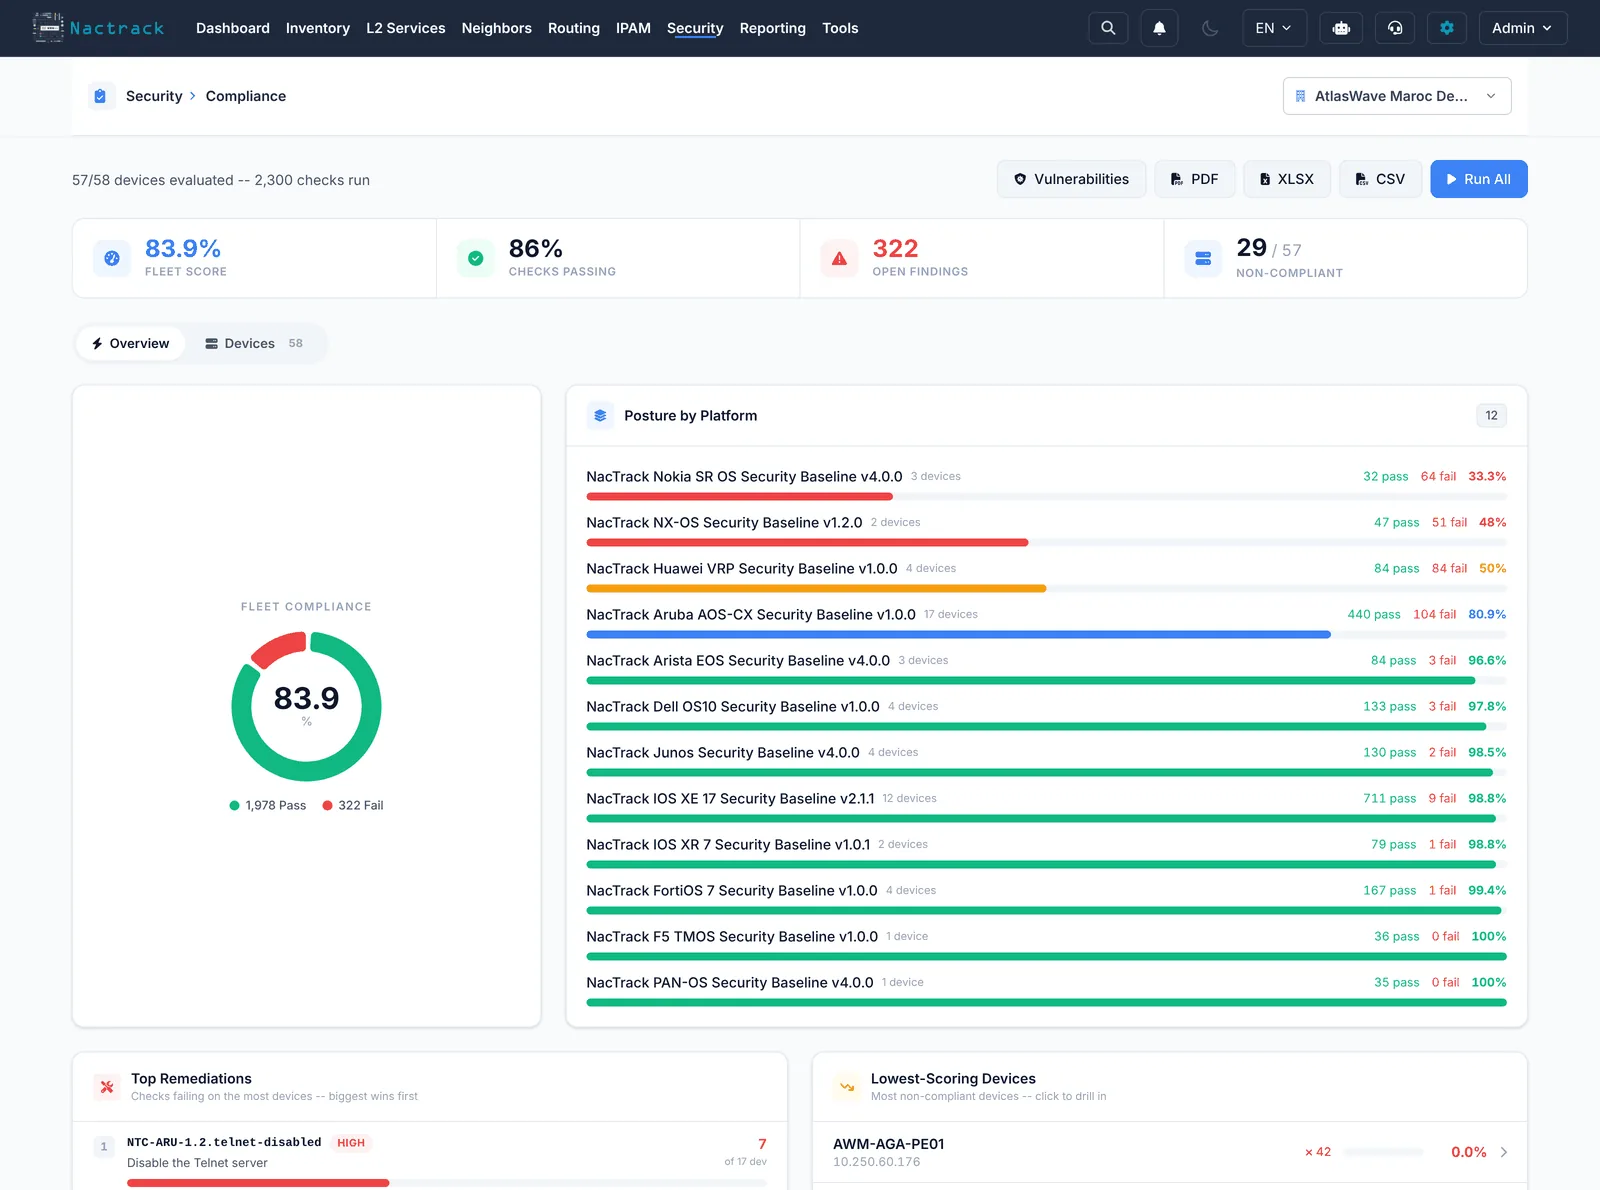
A dated document listing what was found device by device, with the extracts that justify each finding.
The report is yours. You can pass it internally, to your management or to your auditor, without asking us.
What the report contains
Real inventory
Exact models and software versions, site by site, as they are rather than as they are supposed to be.
Vulnerability exposure
The devices reached by published vulnerabilities, matched by exact version rather than by model.
End of support
Hardware past vendor support, with dates, usable to defend a replacement budget.
Hardening gaps
Telnet, SNMP, administrative access, logging. Each gap named by its rule, with the extract that triggers it.
Documentation gaps
What the devices report seeing, compared to what you thought you had. This is often the part that surprises most.
Nothing else
No penetration testing, no changes, no commercial recommendation dressed up as a technical finding.
Request the audit
Tell us the approximate size of your estate and the vendors in it. We propose a date.